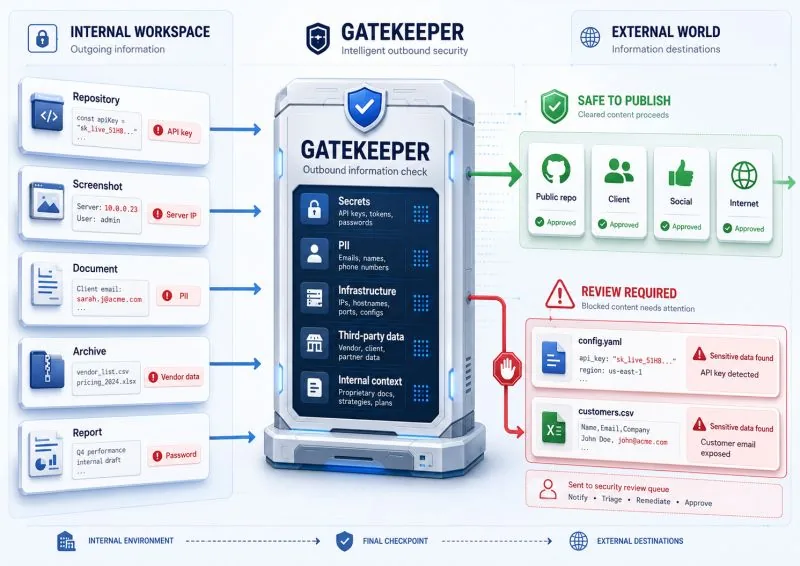
It doesn’t matter whether you work alone or inside a large company. Anything you publish, from a repository to a screenshot or document, can contain something that should never leave your system: an API key, server details, vendor data, internal context, or PII (I cannot help but recall a local mem with one of the company - “It’s P2!” - if you read this and you know, then you know 🤓)
Anyways, the problem is rarely a lack of care -> It is rather volume and confidence. When you handle enough files, reports, commits and screenshots, sooner or later you stop checking every detail as carefully as you think you do.
That is why I like the idea of a Gatekeeper: a final layer that scans outgoing information, flags sensitive content and asks for a second look before anything becomes public. It will never replace human judgement, and it should not. Its job is simpler: catch the things you missed. The more information you produce, the more useful that last checkpoint becomes.