I keep seeing the same problem in companies of a different size: People receive access to repositories, dashboards, cloud accounts, and internal systems, then change roles, move between teams, or leave the company while those permissions remain active.
Over time, some employees and contractors accumulate access they no longer need, creating unnecessary risk and making abuse much easier.
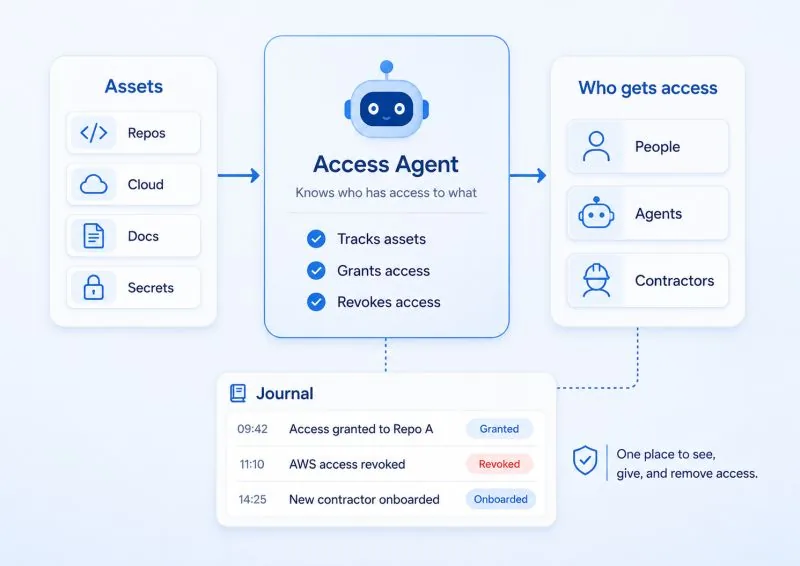
An access agent can maintain a live map of: - who has access - what assets exist - why access was granted - when access was last used - when access should be removed
It can issue permissions during onboarding, review them automatically, and revoke them when a role changes or a person leaves.
This makes Zero Trust operational: everyone receives only the access required for their current work and keeps it only while it remains necessary. If you run a company that cannot afford a serious leak, assuming it will never happen is a dangerous bet; sooner or later, forgotten access becomes someone’s opportunity 🦜